Security
CTF Army Knife
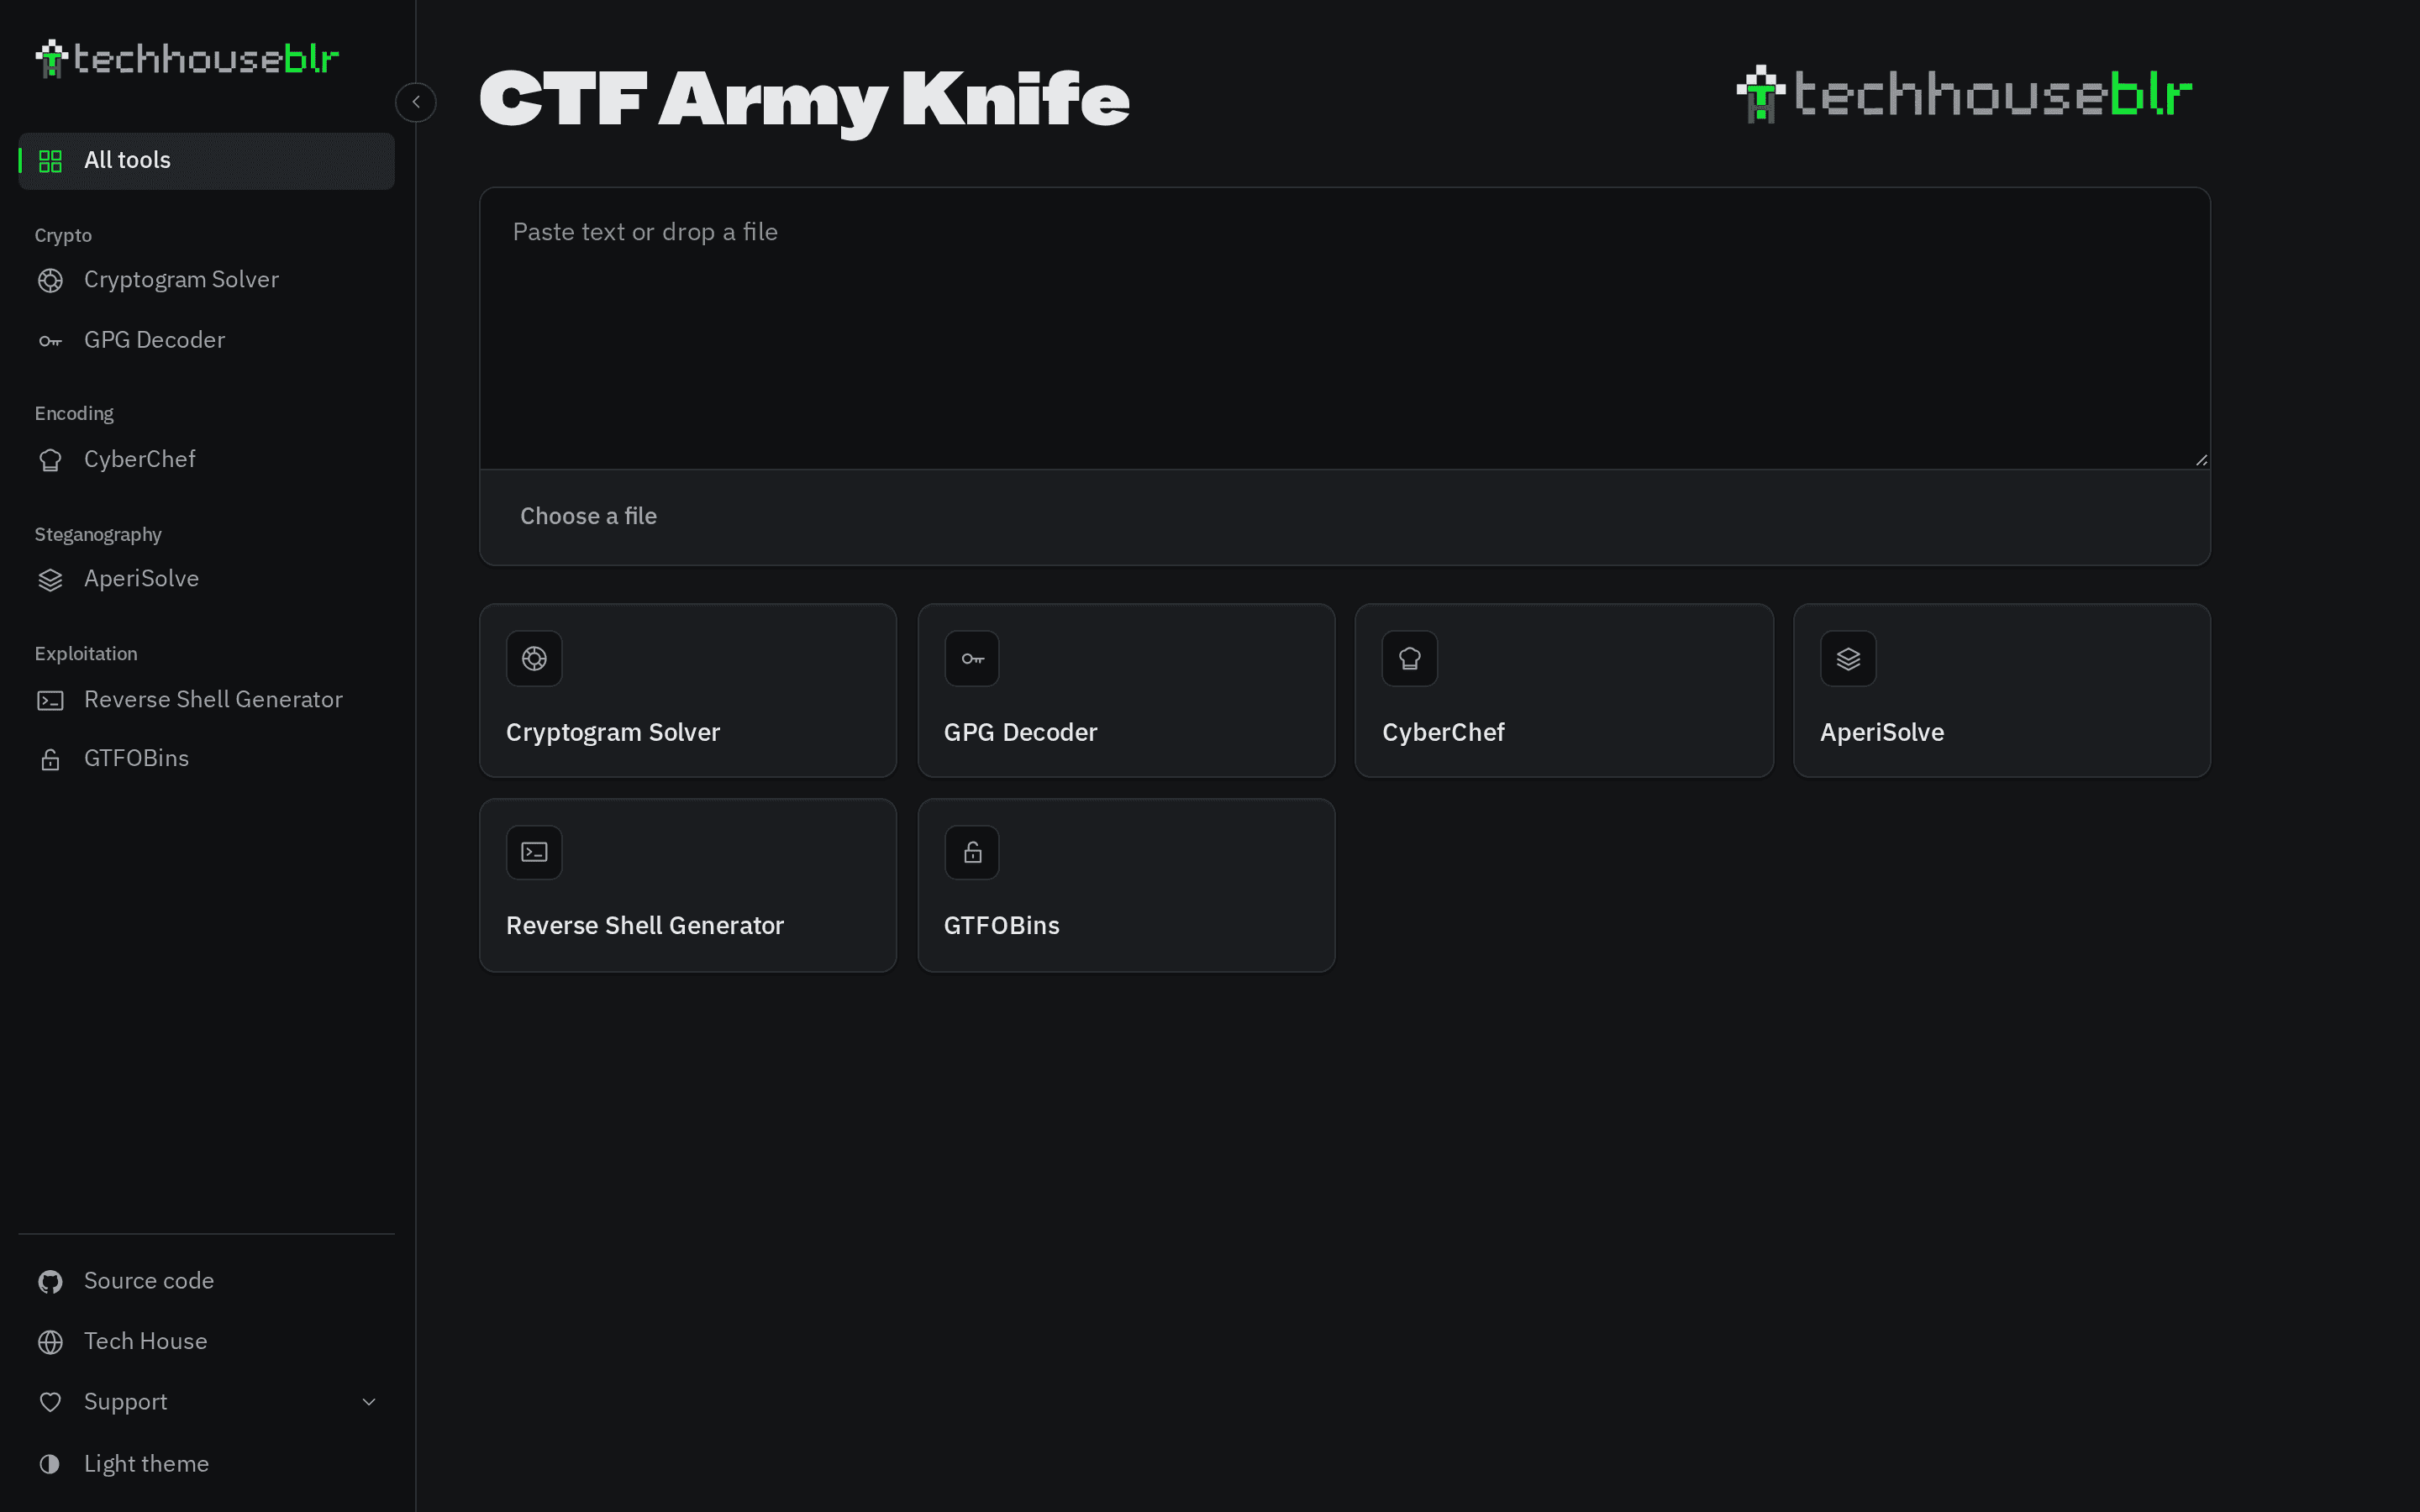
A Swiss army knife for CTFs. Crypto, encoding, steganography and exploitation tools in one self-hosted web app. Paste or drop a file and the dashboard suggests the right tool for it.
AperiSolve 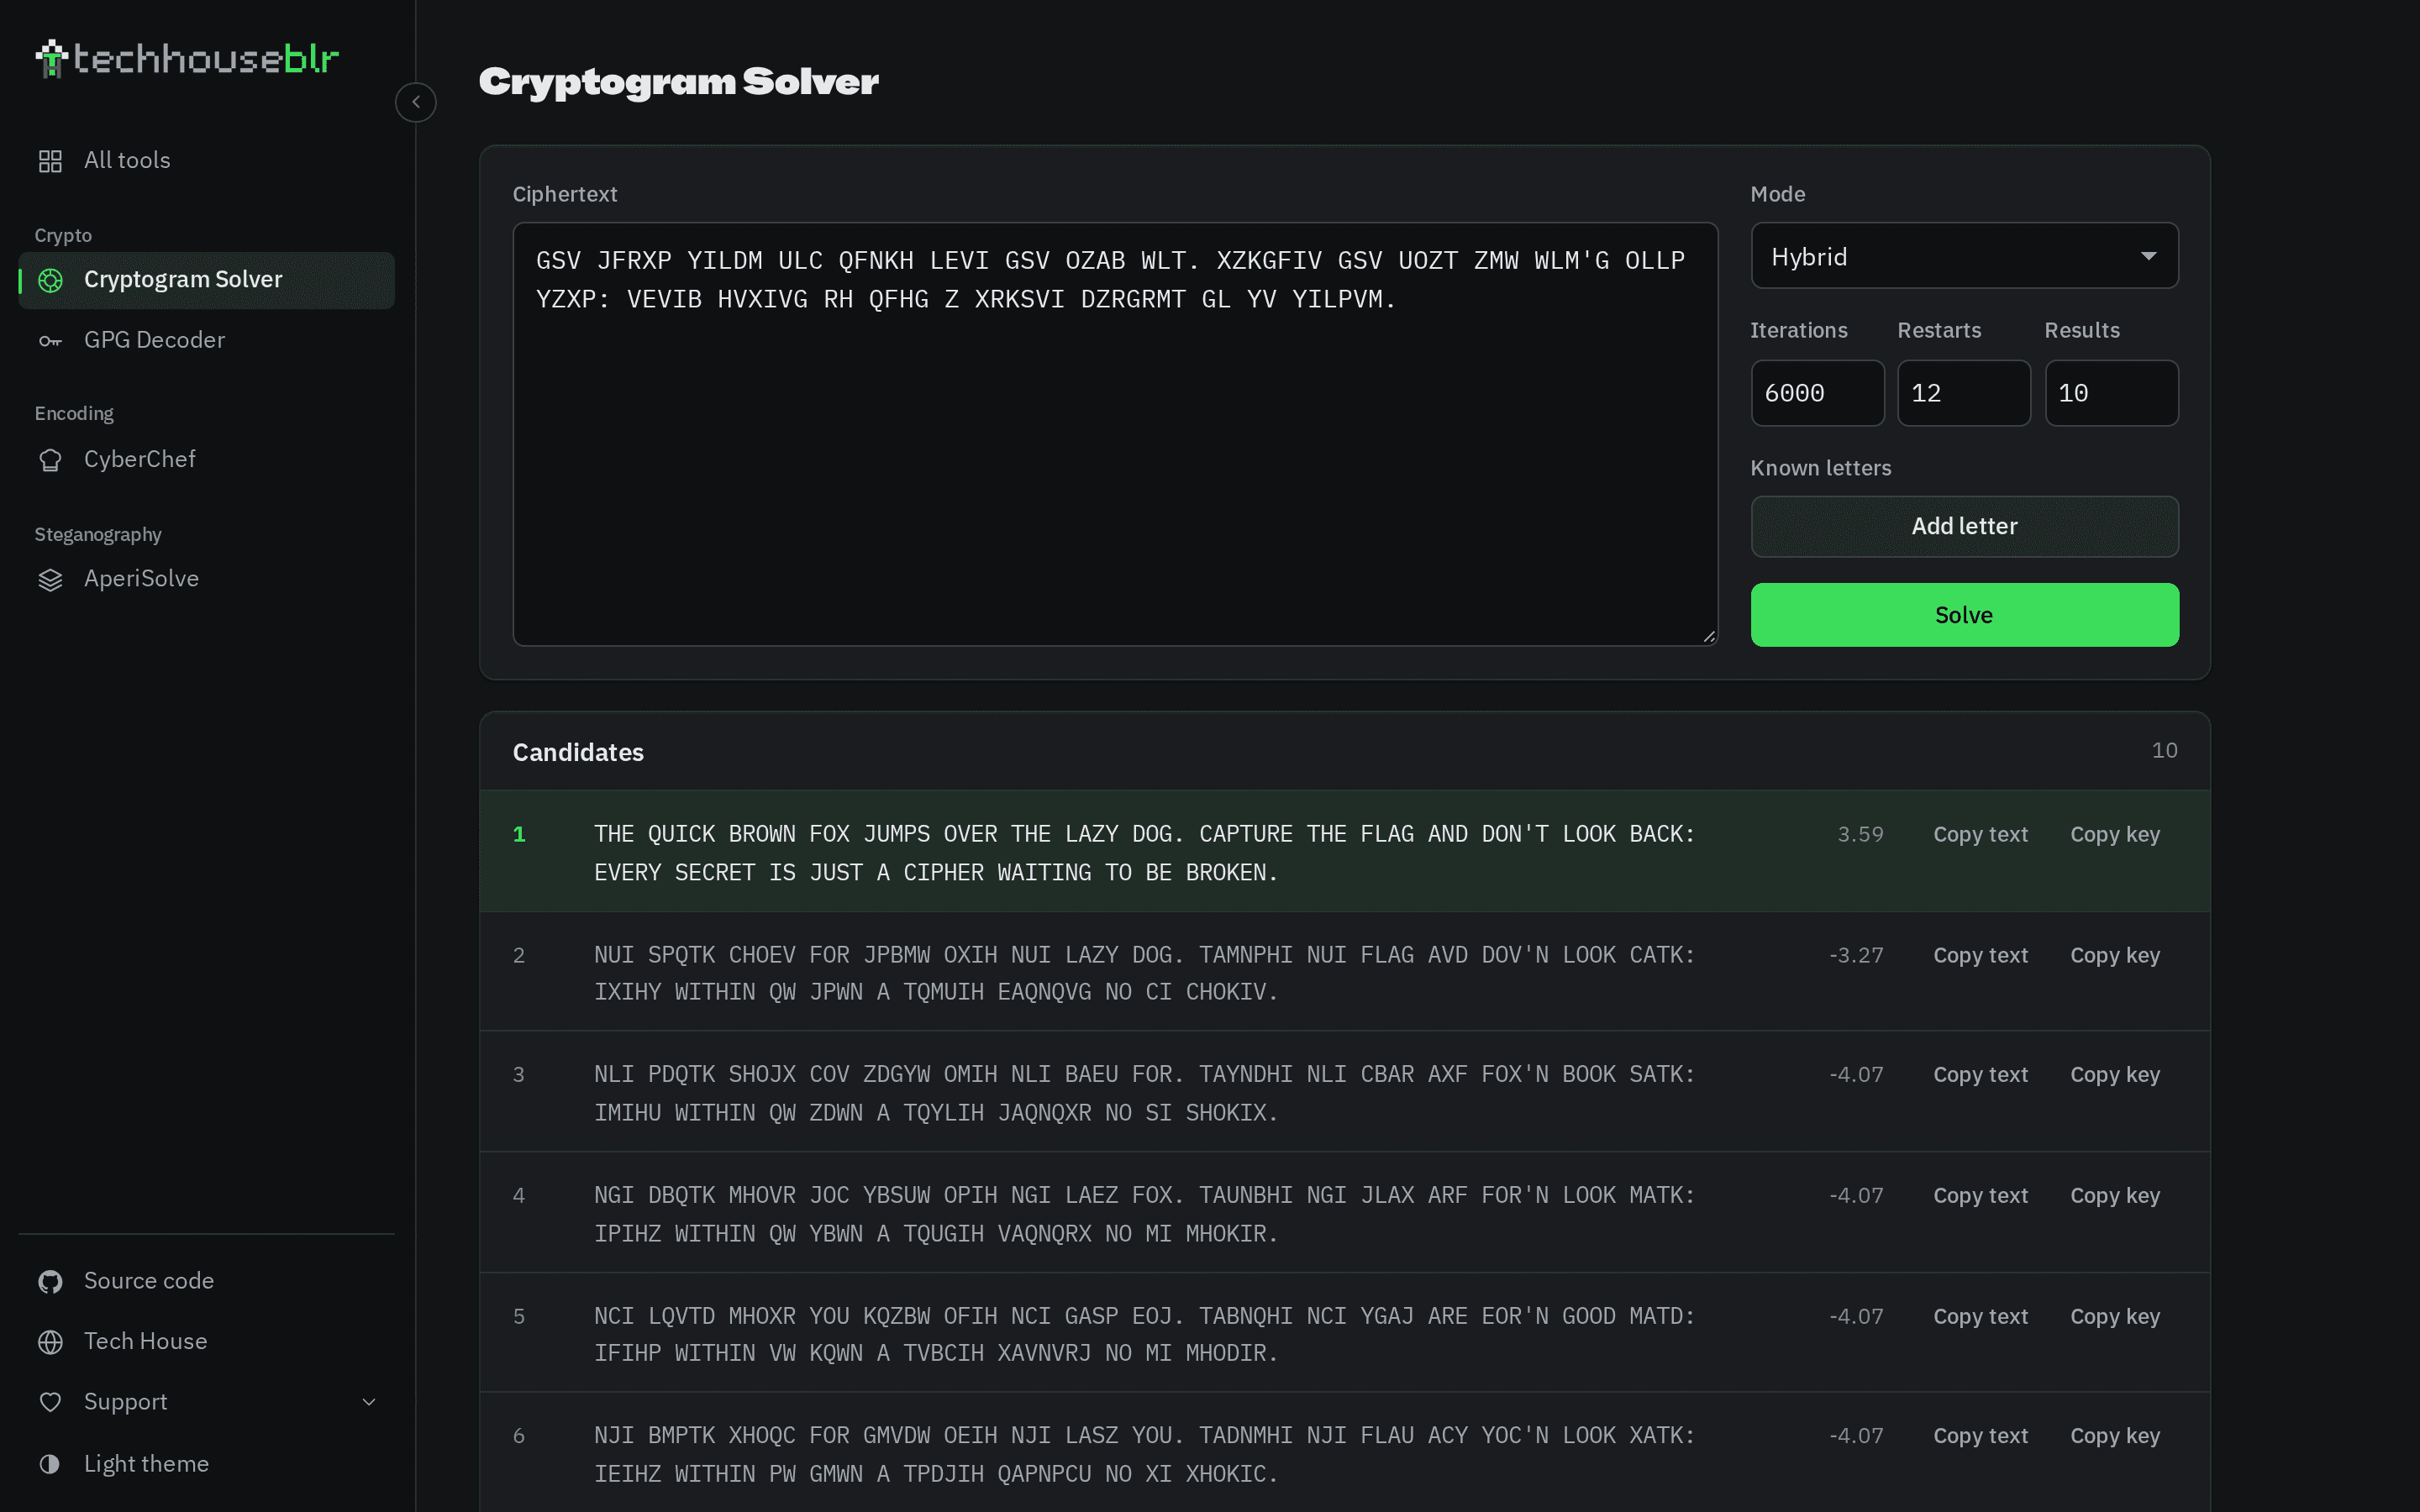
Cryptogram Solver 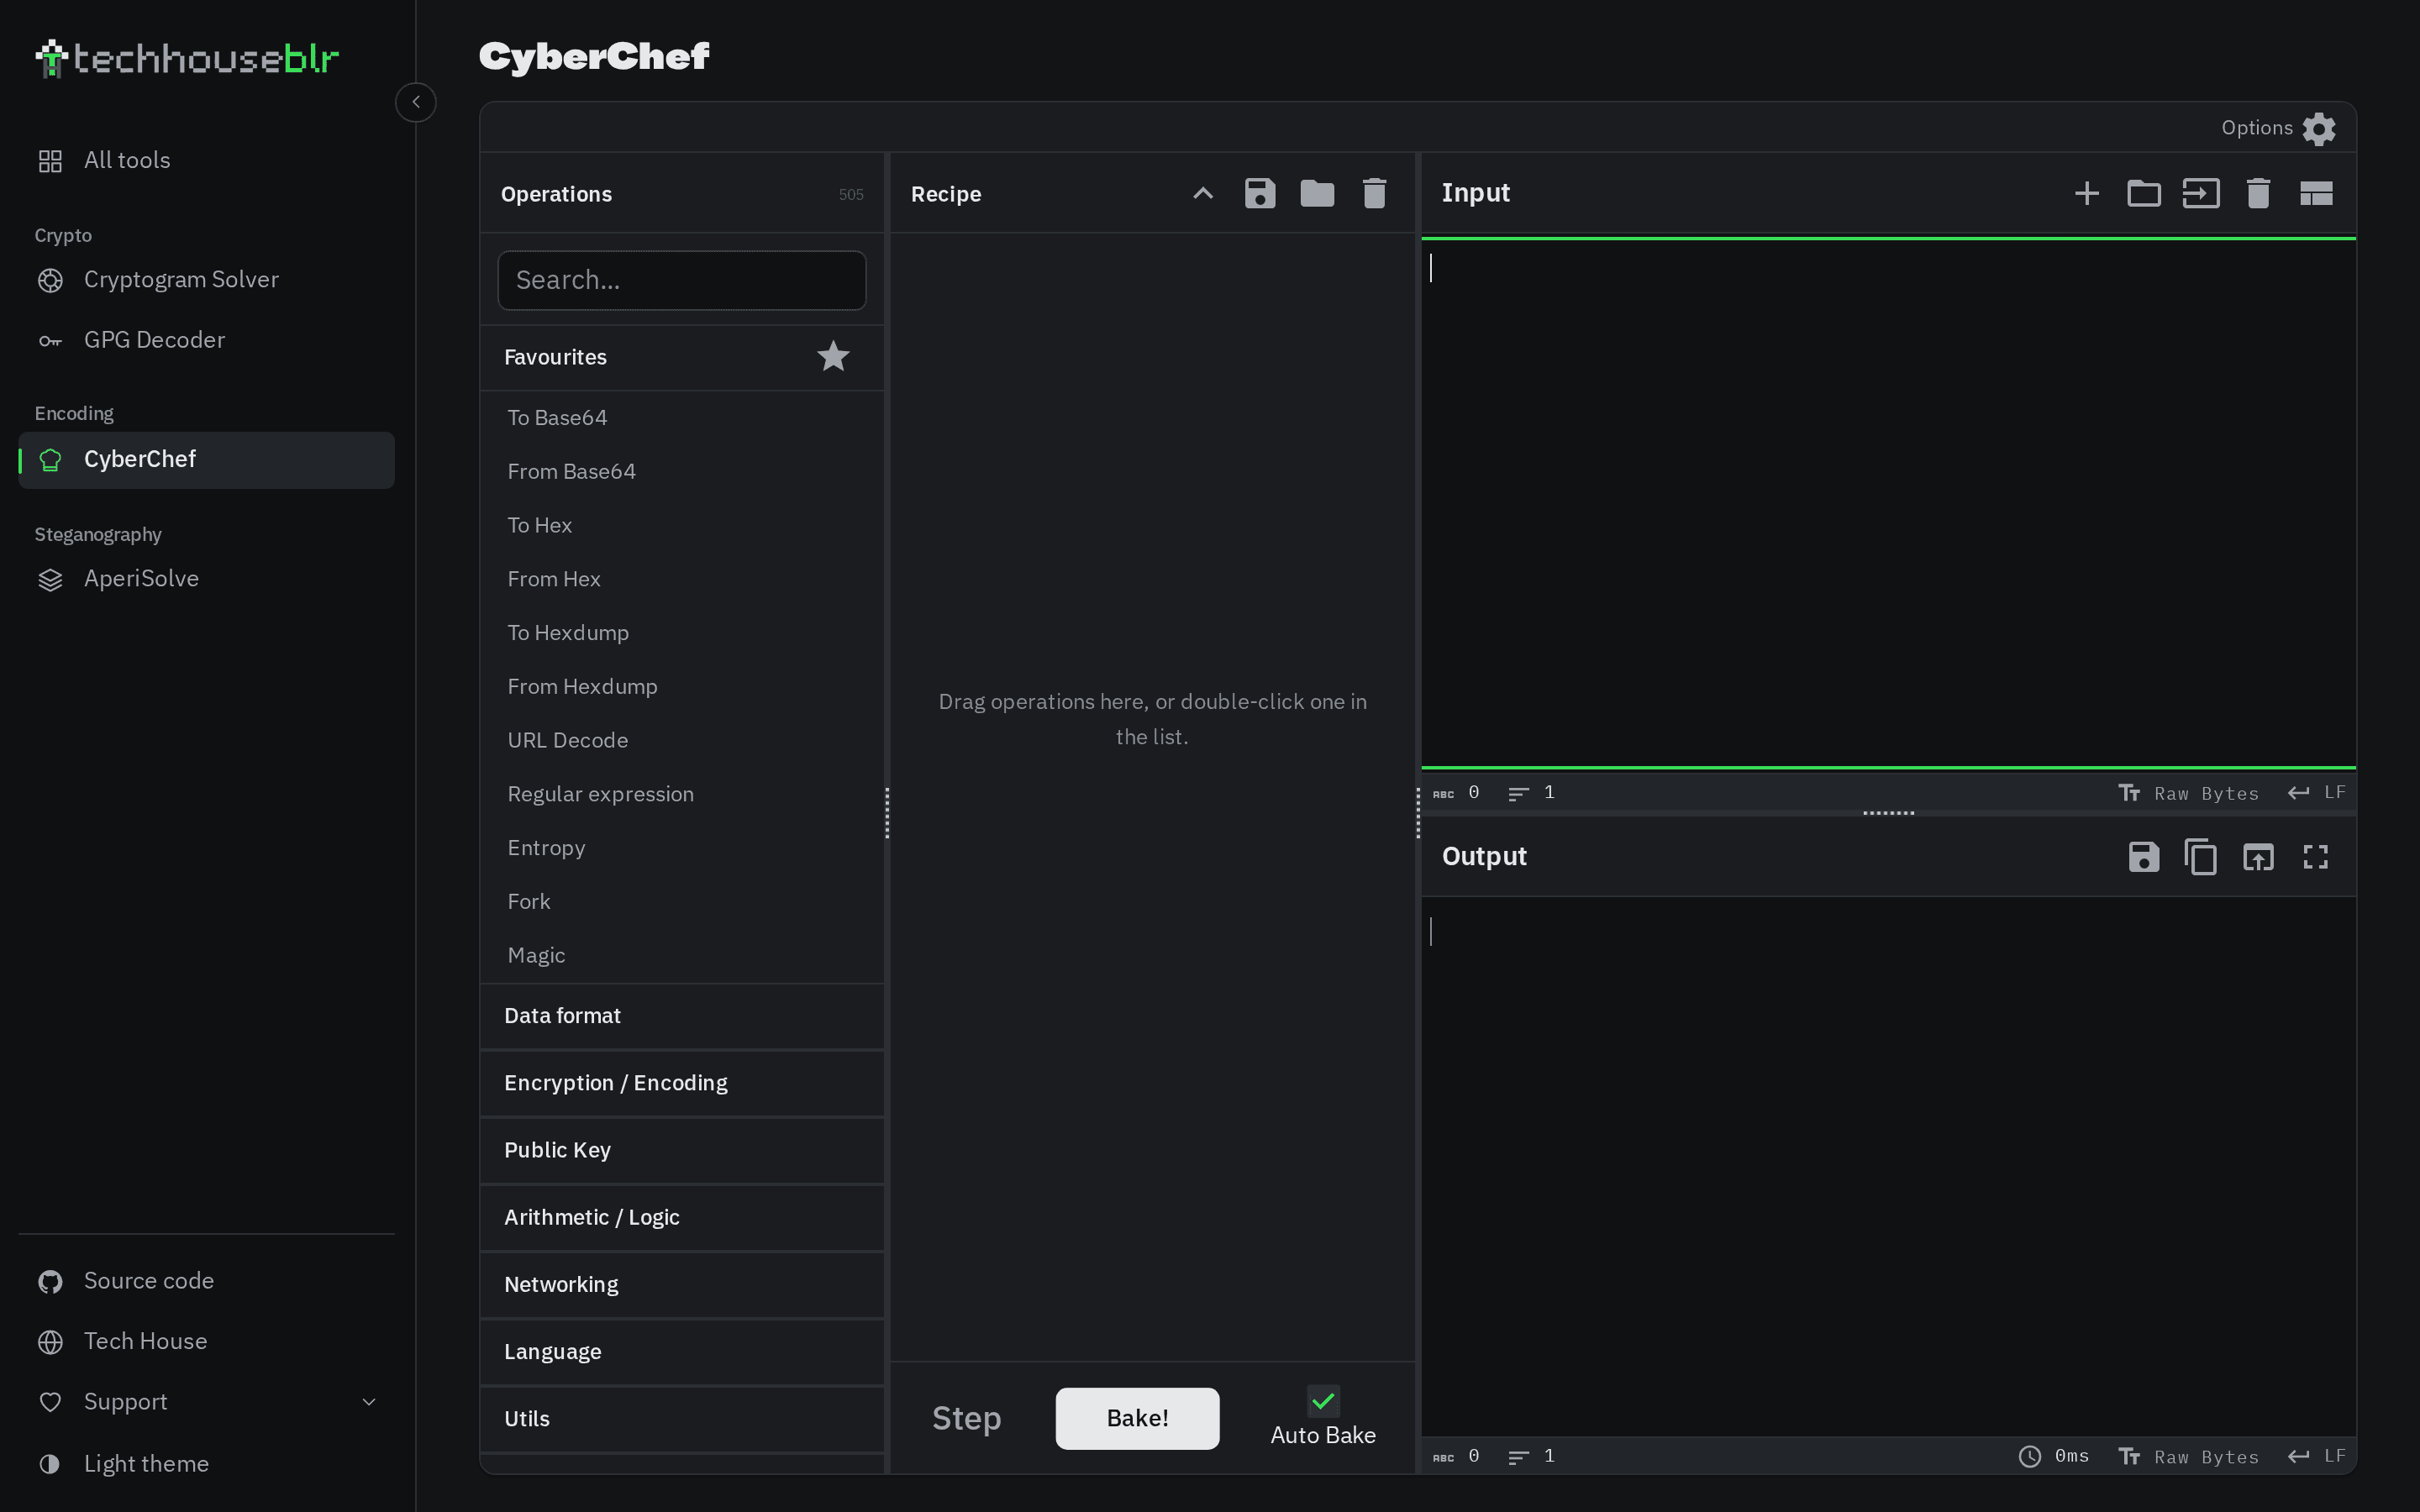
CyberChef 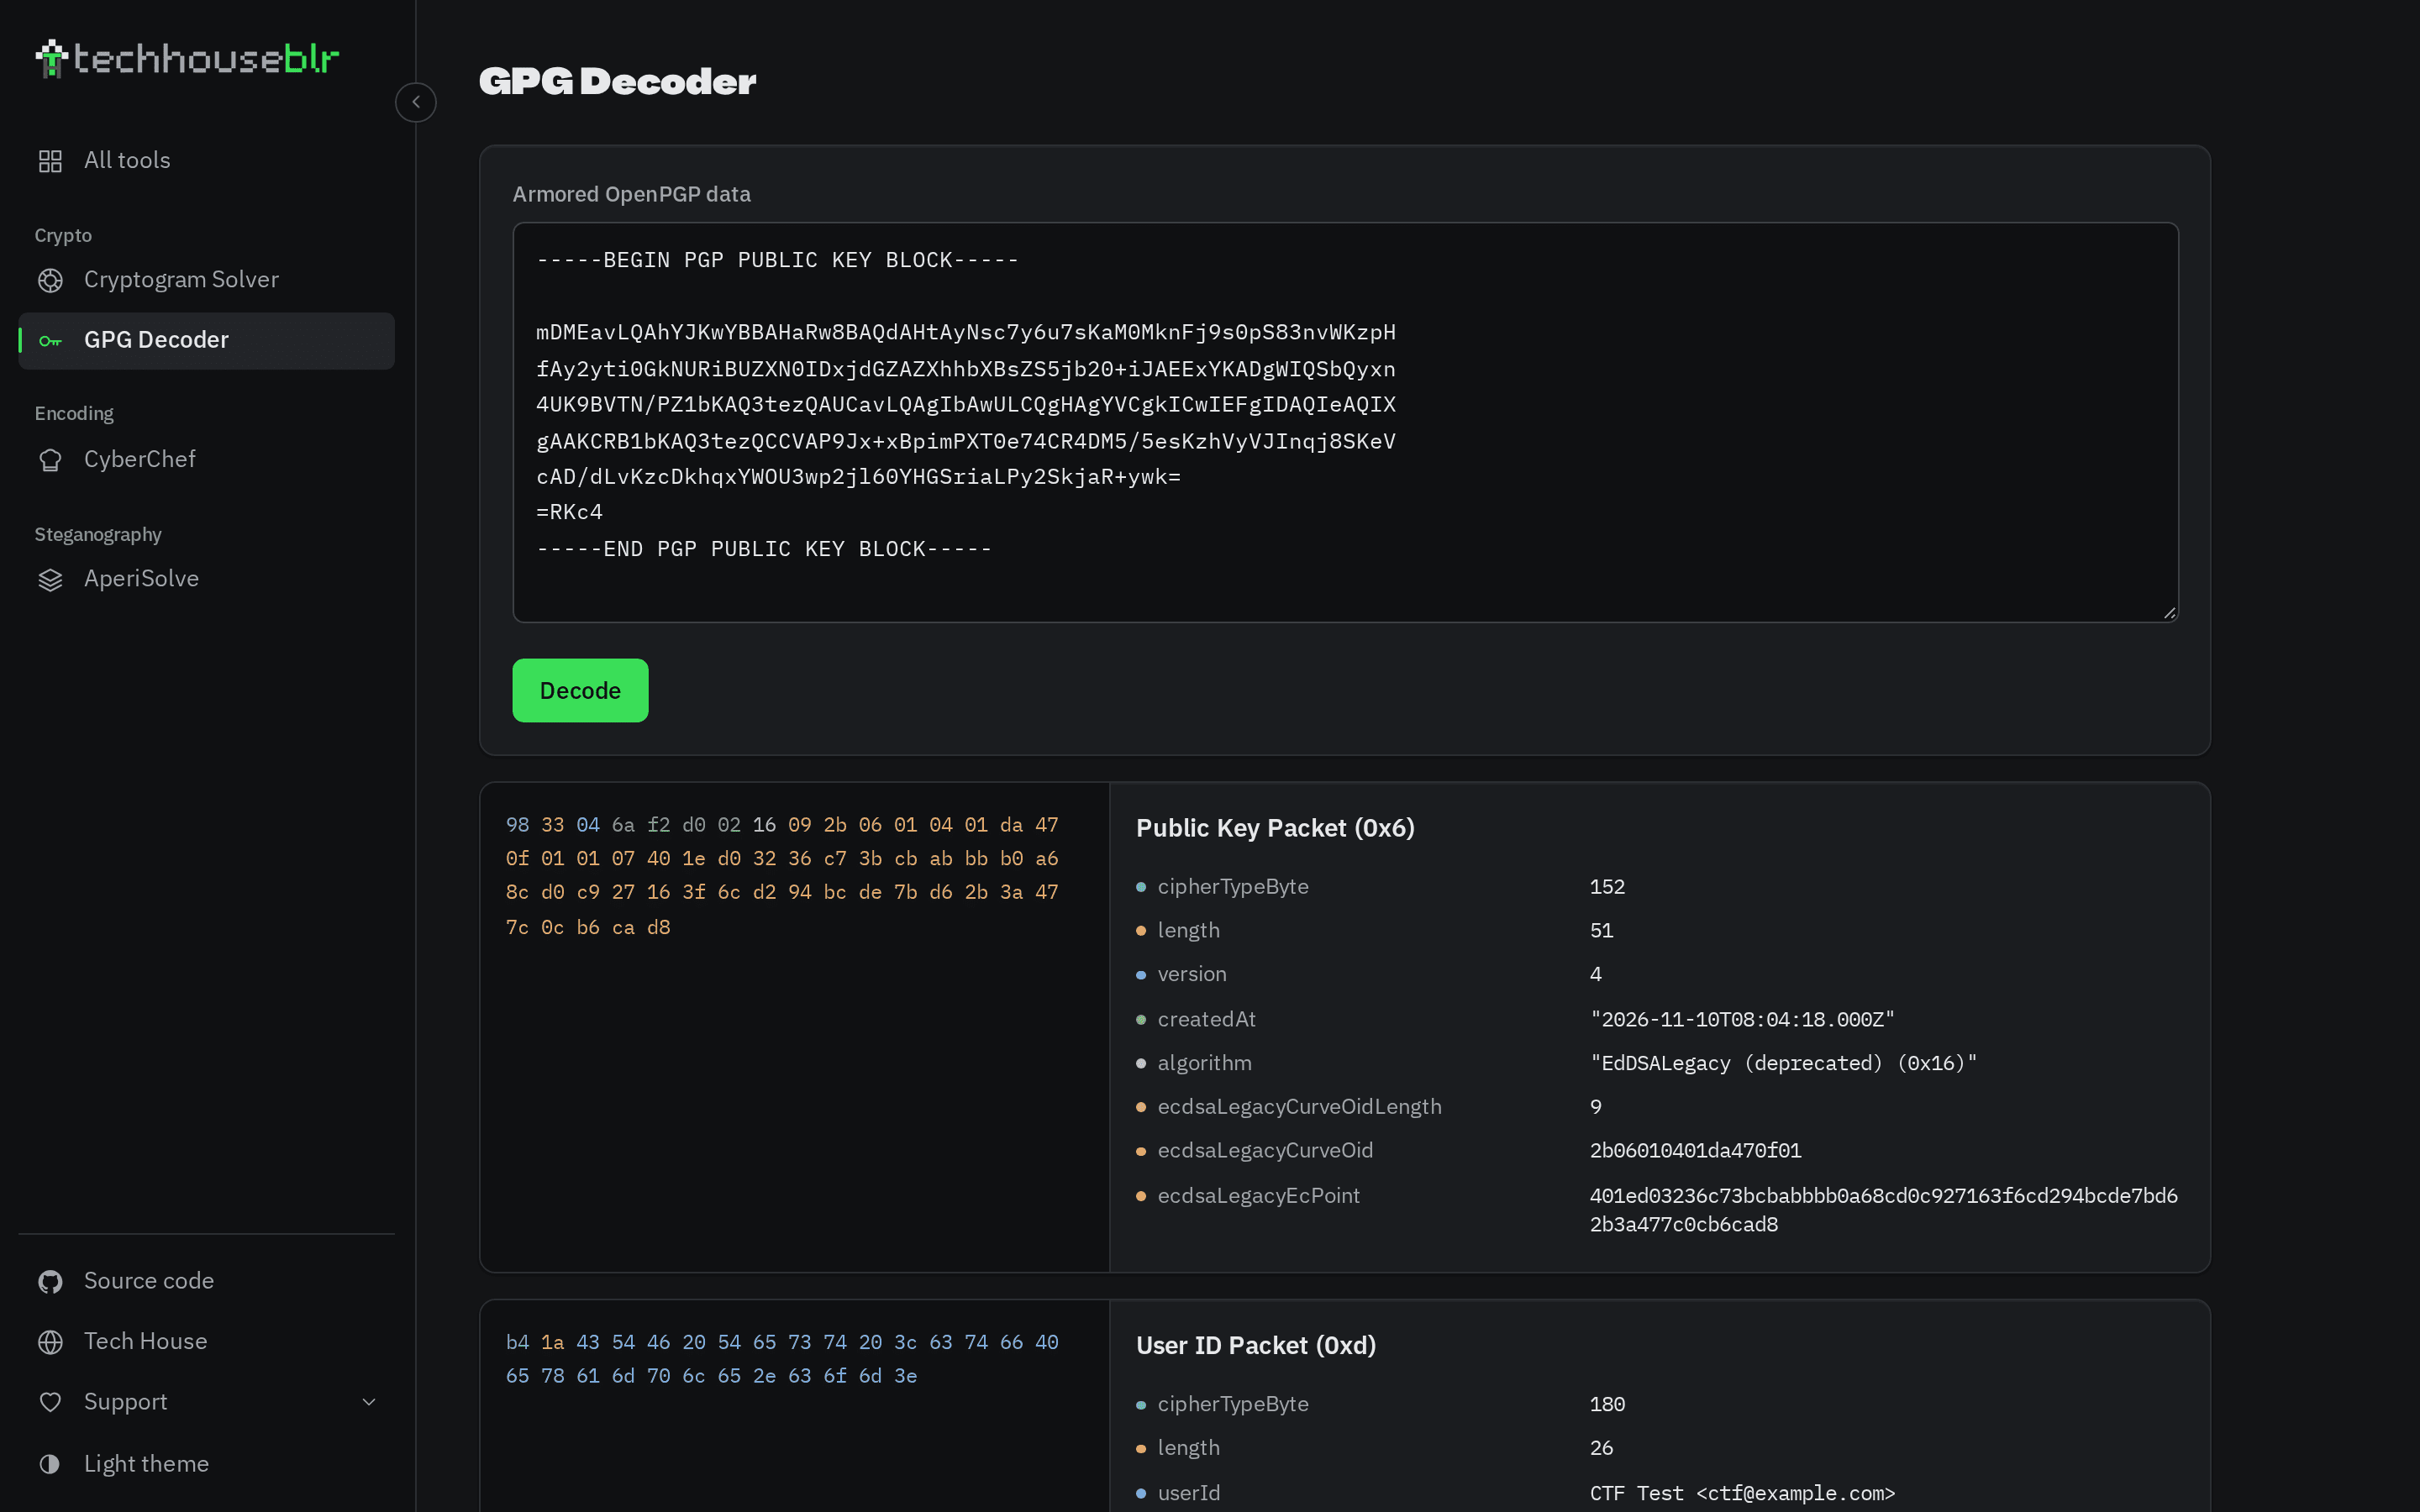
GPG Decoder
Tools
| Tool | What it does | Runs in |
|---|---|---|
| Cryptogram Solver | Break substitution ciphers with frequency analysis and simulated annealing. | API |
| GPG Decoder | Inspect OpenPGP packets with a colour-matched hex view. | BROWSER |
| CyberChef | The full CyberChef catalogue, themed and served locally. | BROWSER |
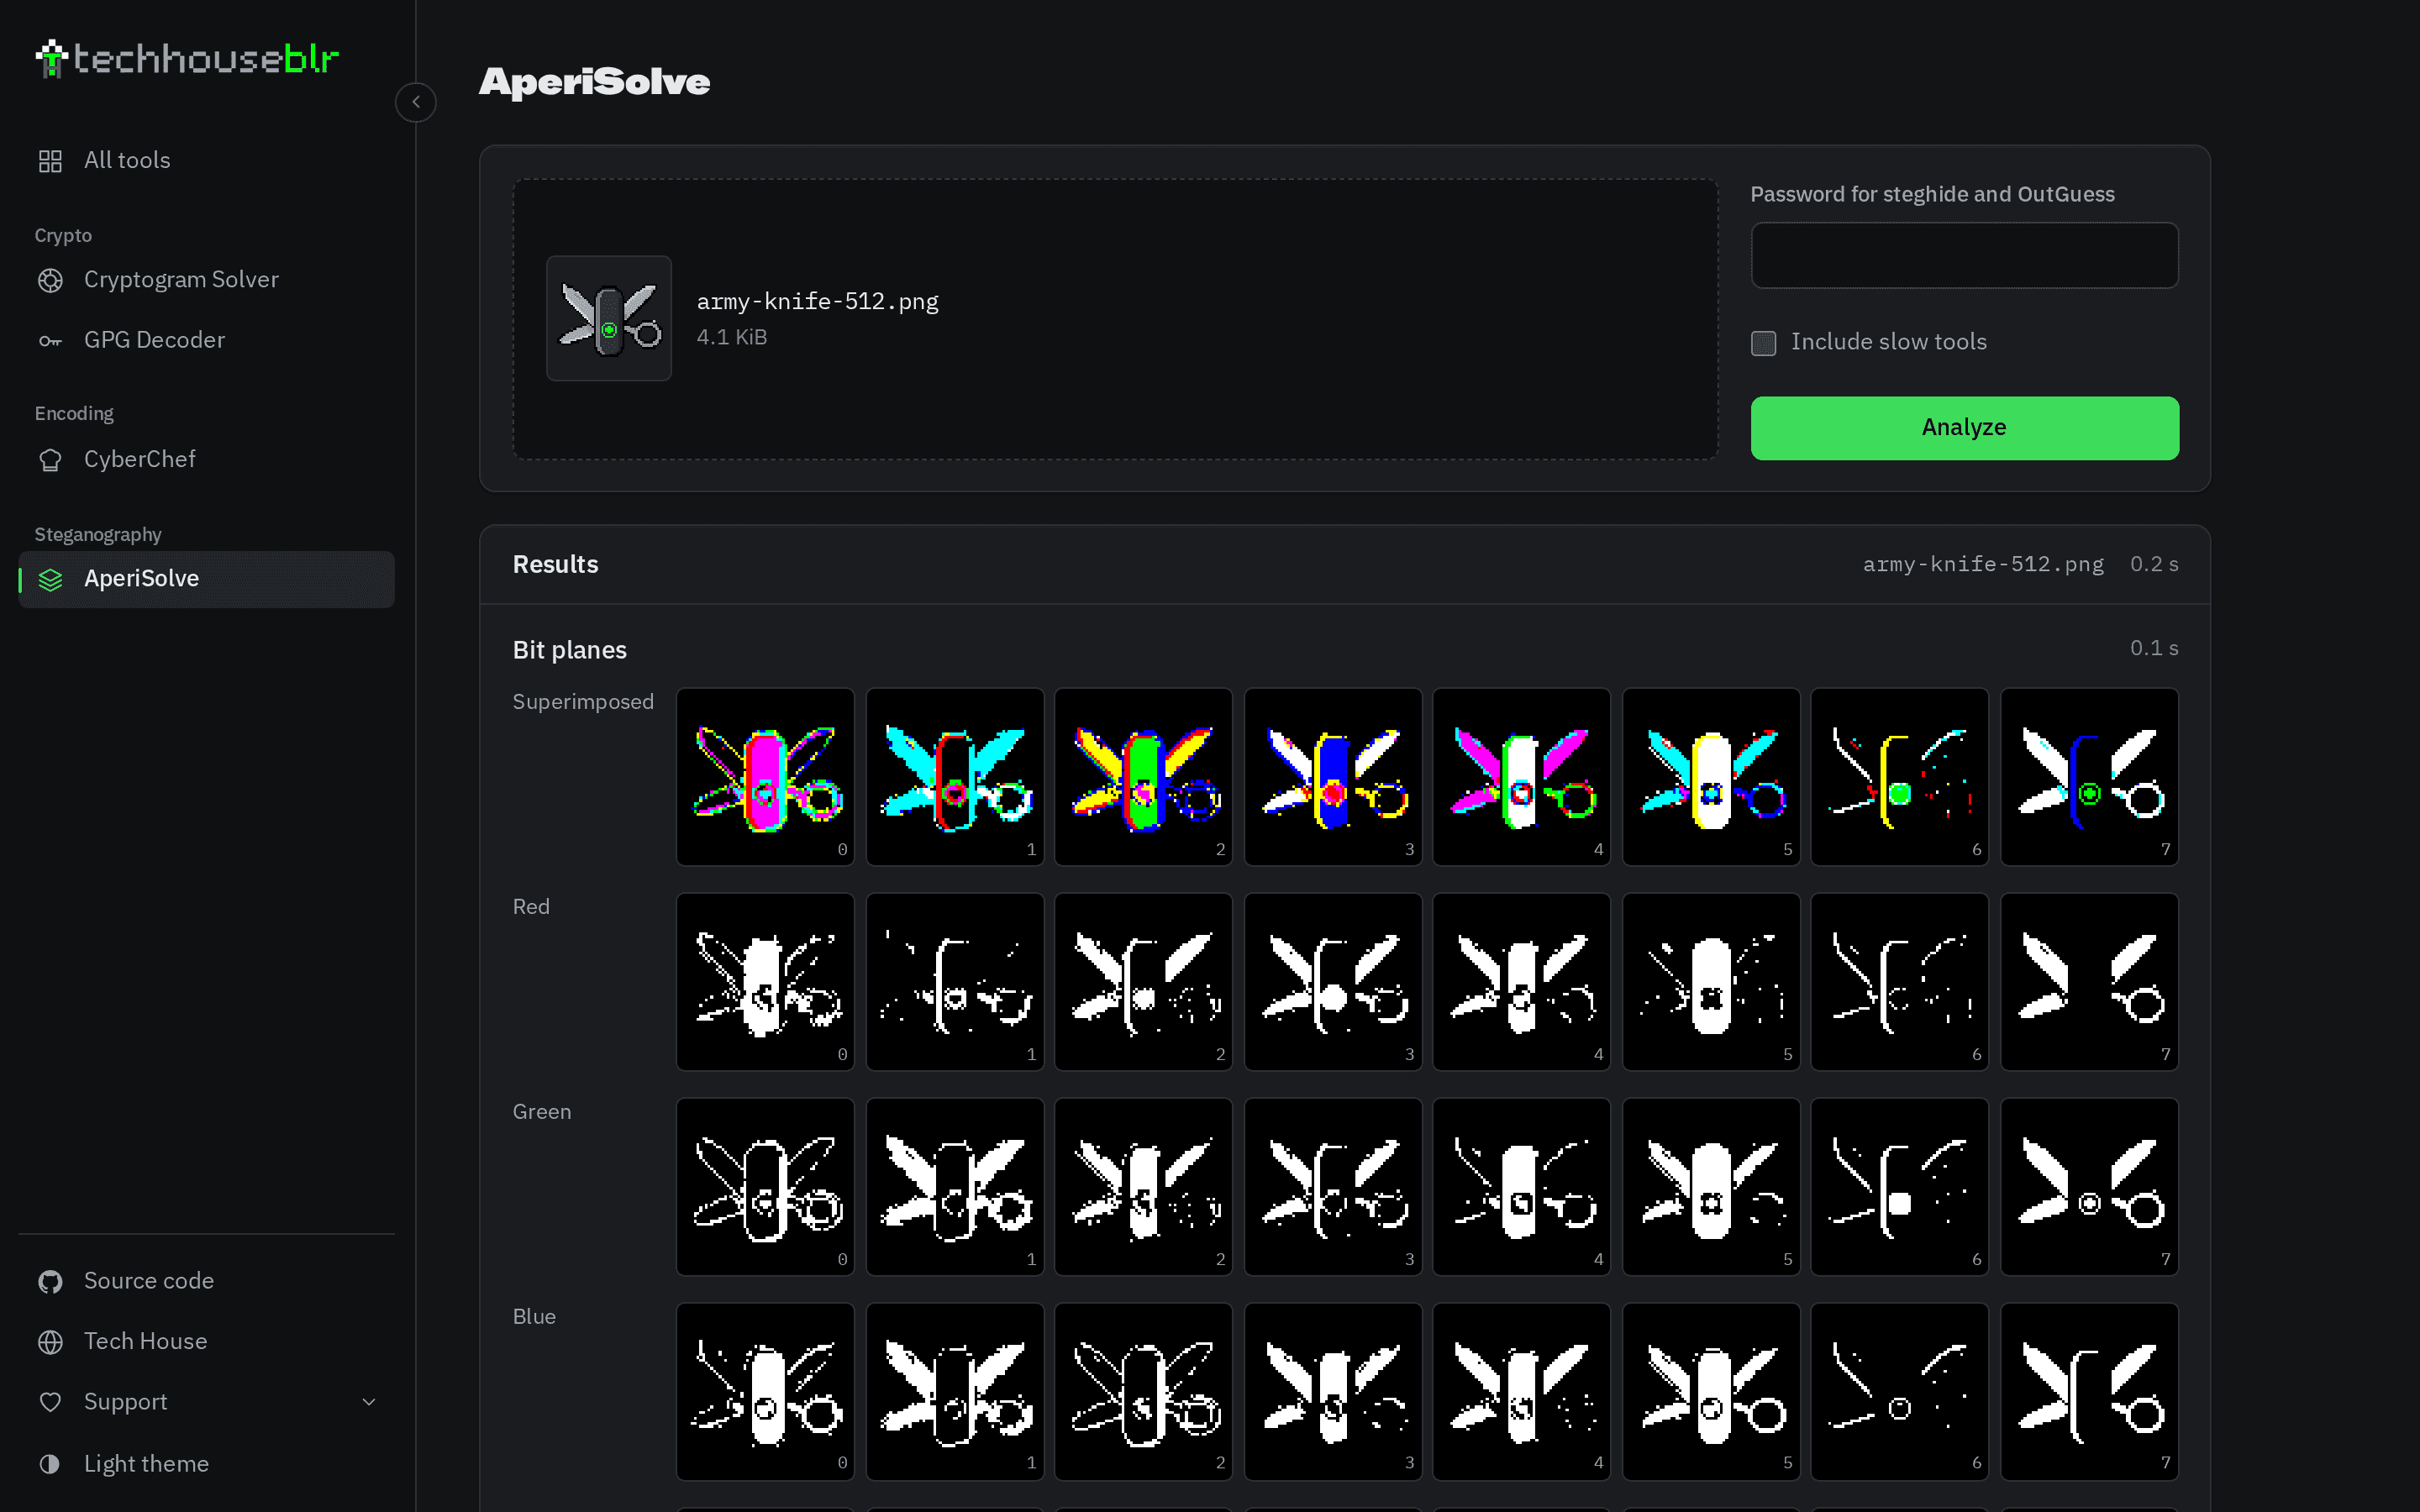
| AperiSolve | Image steganography: bit planes, metadata and a suite of extraction tools, streamed live. | API |
| Reverse Shell Generator | Reverse, bind, MSFVenom and HoaxShell payloads with matching listeners. | BROWSER |
| GTFOBins | Searchable GTFOBins index, filtered by function and privilege context. | BROWSER |
How it works
Tools are either browser-only, where all the logic ships to the client, or API-backed, where they call a FastAPI backend. The browser only ever talks to the Next.js web container, which proxies /api/* to the API.
The API isn't published to the host. Every external program it runs (binwalk, zsteg, steghide, ExifTool and others) goes through a sandbox: no shell, hard CPU, memory, file-size and time limits, in a throwaway workspace on a capped in-memory tmpfs, so an extraction bomb fails instead of filling the disk.
The whole thing runs with a single docker compose up --build.
License & credits
Released under the GNU General Public License v3.0.
Built on the shoulders of: